Data Protection
Cybersecurity Resilience: Have you been focusing on the right things?
Traditional security tools protect networks - not the data itself. This post explains why file-level encryption and true data resiliency are now essential to surviving modern cyberattacks.
Walk into any modern business and you will see layers of protection:
- Firewalls
- MFA
- VPNs
- DLP
- Endpoint detection
- Server hardening
- SIEMs
- Offline backups
Most companies have spent years building strong defenses.
But here is the hard truth:
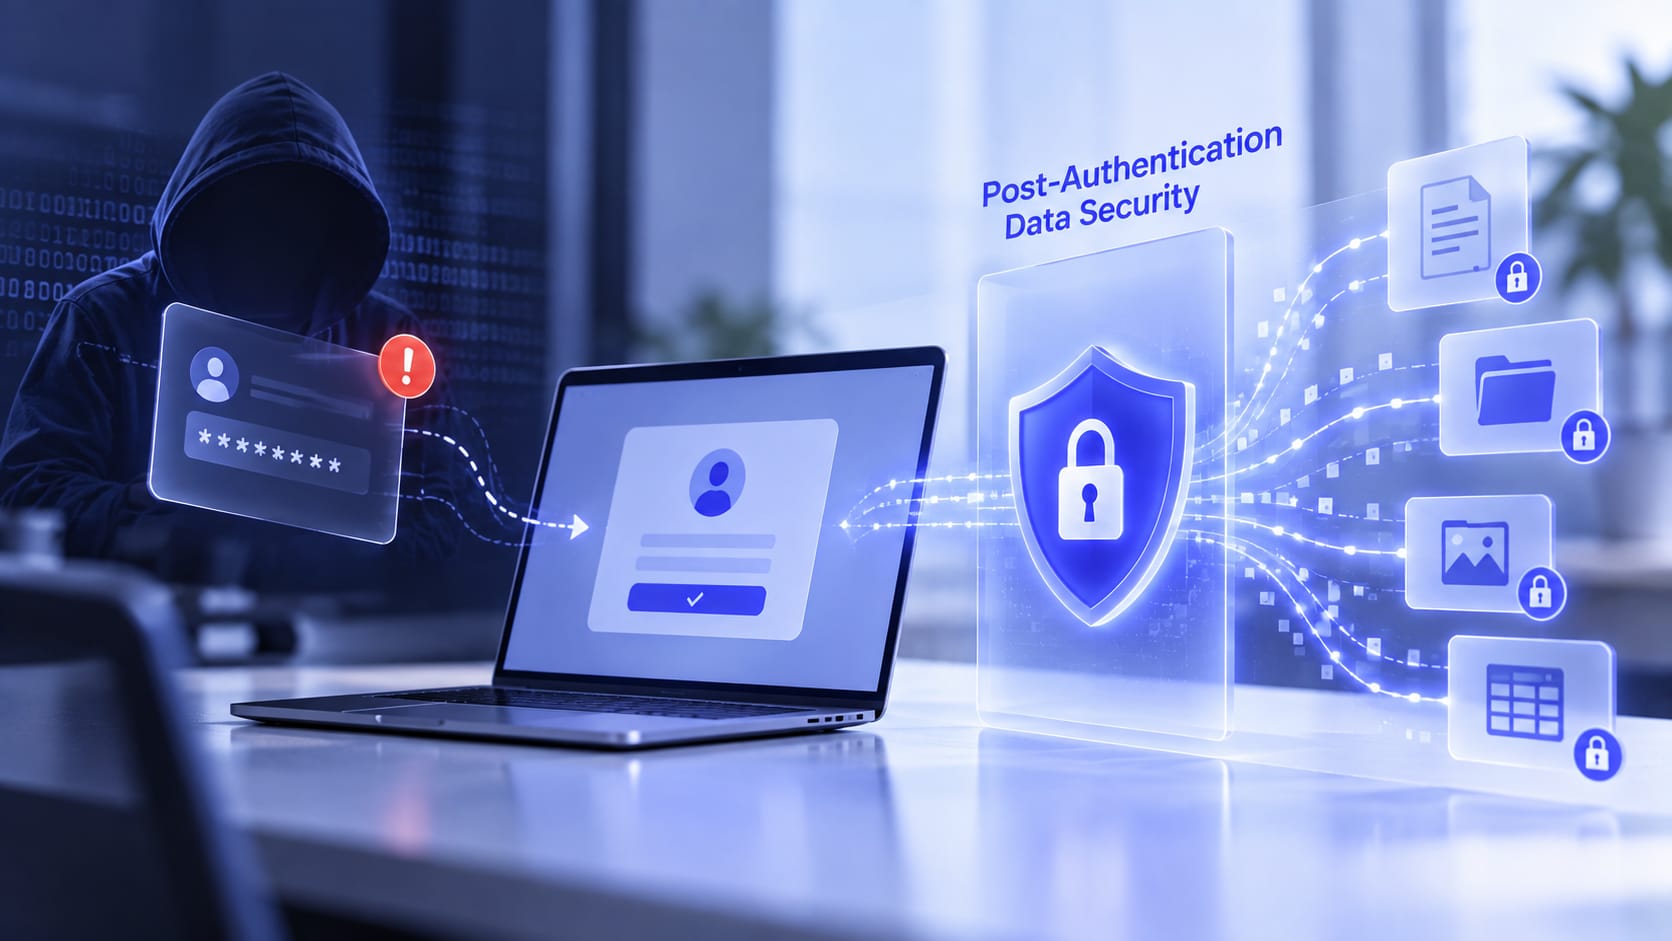
Those layers were never designed to protect data after a valid login.
74% of data theft now occurs post-authentication - after an attacker has already cleared every control in the stack. (Verizon Data Breach Investigations Report 2024)
As Gary Clark, Principal Cybersecurity Consultant at Yearling Solutions, explains:
“We’ve built a lot of resiliency in cybersecurity - identity resiliency, endpoint resiliency, technology resiliency. But where we haven’t spent enough time is with data resiliency.”
That missing layer - protecting the data itself after access is granted - is what leaves even well-funded security programs vulnerable.
It is the gap that Post-Access Data Security (PADS) was built to close.
The Pre-Boom Mindset - and Why It Leaves Data Exposed
Clark introduces a simple but powerful framework: pre-boom vs. post-boom.
- Pre-boom: prevention, detection, containment
- Post-boom: what happens after the breach, when data starts moving
“We’ve conditioned ourselves to think that if we implement all of the pre-boom controls, we’ll have the resiliency we need,” Clark says.
But that assumption breaks under modern attack patterns.
Security teams have built resilience around the controls protecting the data - instead of building resilience into the data itself.
A simple analogy makes this clear:
Banks didn’t stop robberies by reinforcing the glass. They added dye packs to the cash.
Even if the money is stolen, it becomes worthless.
That is exactly what Post-Access Data Security does.
Even when an attacker:
- Authenticates
- Moves through your environment
- Exfiltrates files
…the data remains:
- Encrypted
- Unreadable
- Unusable
The breach event occurred.
The breach outcome didn’t.
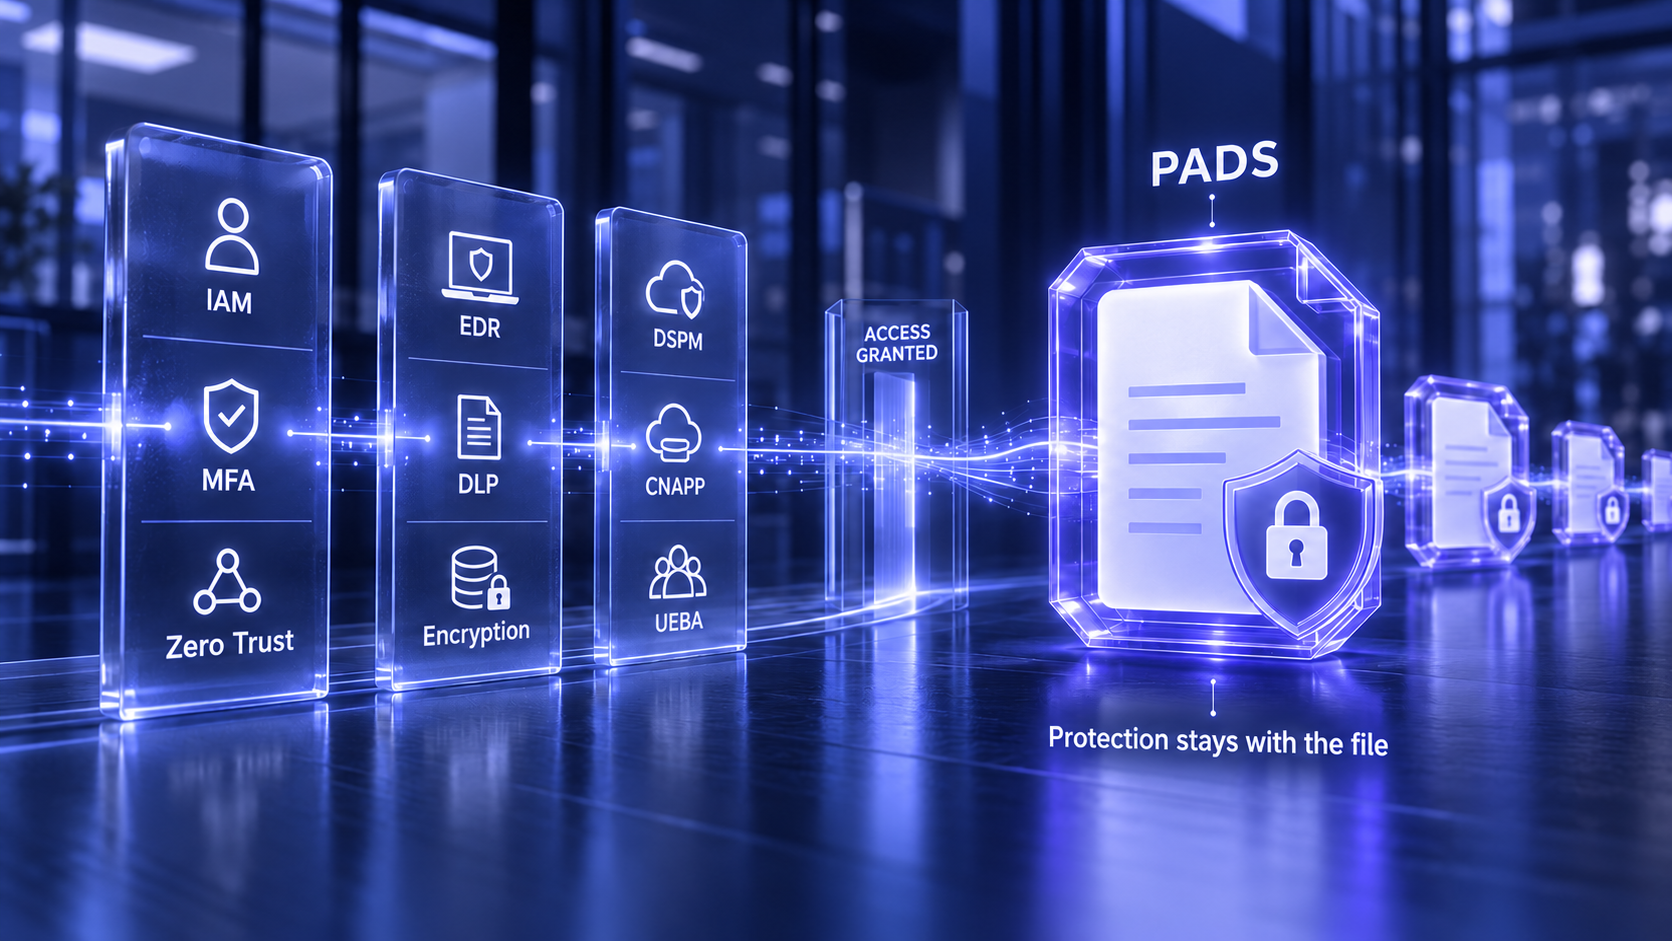
Pre-boom controls - firewalls, MFA, Zero Trust, EDR - govern whether someone gets in.
PADS governs what they can do with the data once they are.
Those are fundamentally different control planes - and the industry has overwhelmingly built only the first.
Exfiltration Happens Before Detection Can
Attackers don’t wait anymore.
“Now as soon as they get an account, they’re exfiltrating data,” Clark explains.
Even with low-privilege access, attackers:
- Pull internal data immediately
- Pivot to additional accounts
- Escalate privileges
Most breaches begin with a legitimate username and password - via:
- Insider threats
- Phishing (now the dominant vector)
Traditional controls can reduce impact.
But none can guarantee protection once:
- Access is legitimate
- Behavior appears normal
- Data leaves through approved workflows
Once data leaves your environment, control is gone - unless the data itself is protected.
PADS changes this.
It does not wait for detection.
It assumes compromise - and protects the data anyway:
- Before the breach
- During the breach
- After the breach
Exfiltrated files remain encrypted and unusable, regardless of where they go.
What Post-Access Data Security Actually Means
Encryption has existed in enterprise security for decades.
But too often, it stops at:
- Data at rest
- Data in transit
…and disengages the moment a user logs in.
Clark explains the gap:
“You have to understand the context of how the data is being used and whether it’s fallen into adverse hands. You don’t want to allow it to be unencrypted if it’s in the wrong place.”
That is what PADS enforces.
Protection is no longer a property of infrastructure.
It becomes a property of the data itself.
A PADS-protected file carries its own policy:
- Who can open it
- On what device
- Under what conditions
If the file:
- Leaves your network
- Is copied to an unapproved device
- Is accessed outside policy
…it remains:
- Encrypted
- Unreadable
- Unusable
The attacker authenticated - and still walked away with nothing.
This is the shift from pre-boom thinking to true data resilience.
Where PADS Changes the Outcome by Industry
Manufacturing
From CAD designs to production schedules, data constantly moves between plants and partners.
A single compromised credential can expose:
- Proprietary processes
- Customer IP
With PADS:
- Files only open for approved users, devices, and locations
- IP remains protected - even outside the organization
Healthcare
Hospitals exchange massive volumes of sensitive data daily.
Compliance frameworks (HIPAA, HITECH) are necessary - but not sufficient.
Major breaches (Anthem, Change Healthcare, CommonSpirit Health) proved that.
With PADS:
- Data stays encrypted across systems
- Unauthorized access results in unusable data
- Compliance becomes a floor - not a ceiling
Finance
Credential compromise is the dominant breach vector.
With PADS:
- Authentication ≠ data exposure
- Files remain encrypted even after login
- Breaches do not automatically become disclosure events
Aerospace & Defense
Sensitive engineering and CUI data must remain protected beyond the perimeter.
PADS ensures:
- Access controls travel with the data
- Only approved contexts allow decryption
- CMMC goals are met without workflow disruption
Energy & Utilities
Critical infrastructure data moves across contractors and regulators.
PADS enables:
- Instant access revocation
- Persistent protection across partners
- Stronger regulatory assurance
Frictionless by Design
No security strategy works if it slows down the business.
“Users just want to do their work,” Clark says. “Cyber tools should be as frictionless as possible.”
PADS embeds protection into normal workflows:
- No change to how users save, send, or access files
- No additional friction for legitimate use
Only when policy is violated:
The file simply doesn’t open.
Protection is:
- Invisible to authorized users
- Absolute against attackers
The Business Reality
Every organization faces the same core risk:
- Intellectual property
- Customer data
- Operational records
- Financial information
All are valuable - and all are targeted.
As Clark puts it:
“We’re all struggling with the same thing. Whether you have a lot of resources or just a few, focus on what the attacker actually wants - your data and your operations.”
The shift is clear:
- Less focus on building higher walls
- More focus on protecting what’s inside them
Because at some point:
Your environment will likely be breached.
What matters is what happens next.
The Question That Defines Resilience
If someone logs in with valid credentials right now - what actually protects your data?
Perimeter security still matters. Identity still matters. Detection still matters.
But none of it is sufficient if data becomes instantly usable after authentication.
The Bottom Line
Cybersecurity resilience is no longer about preventing entry alone.
It is about ensuring that even when attackers get in:
- Data remains encrypted
- Data remains unusable
- Data remains worthless
Post-Access Data Security is the shift that makes that possible.
Because in a world where breaches are inevitable, the organizations that survive will be the ones whose data is protected after access is granted - not just before.