Data Protection
Cybersecurity Spending Keeps Rising. So Do Breach Losses. That Is Not a Coincidence.
Security spending fails because it only blocks entry, not data loss. Post-Access Data Security (PADS) fixes the ROI by protecting data after login, turning catastrophes into non-events.
Cybersecurity budgets have grown steadily for more than a decade. Boards approve larger line items each year. Security stacks expand. Tool counts rise. Maturity scores improve.
Yet the financial impact of data breaches continues to increase.
This is not a paradox. It is a signal.
Executives are no longer asking whether security teams are working hard or whether controls are deployed correctly. They are asking a sharper, more consequential question:
Which security investments actually reduce loss?
Post-Access Data Security (PADS) exists because most security spending does not answer that question honestly. It focuses on reducing the probability of intrusion while leaving the economics of data exposure largely unchanged.
PADS targets the moment where financial damage actually occurs: after access is granted and data becomes readable.
The Core ROI Problem in Cybersecurity
Most security investments are justified using probabilistic language. Firewalls reduce the likelihood of intrusion. Identity systems reduce unauthorized access. Endpoint tools increase detection confidence. DLP raises alerts when data moves suspiciously.
These controls are necessary. None of them guarantee loss prevention once an attacker is authenticated.
The largest costs of a breach are rarely tied to how access occurred. They are tied to what happened after access succeeded.
Regulatory penalties. Litigation. Incident response. Business interruption. Customer churn. Contractual fallout. Insurance disputes. Long-term brand damage.
All of these costs are driven by one outcome: data exposure.
Security strategies that do not directly prevent data exposure cannot credibly claim to reduce breach loss. They reduce uncertainty. They improve posture. They do not change the economic outcome when trust fails.
PADS Changes the Economics of a Breach
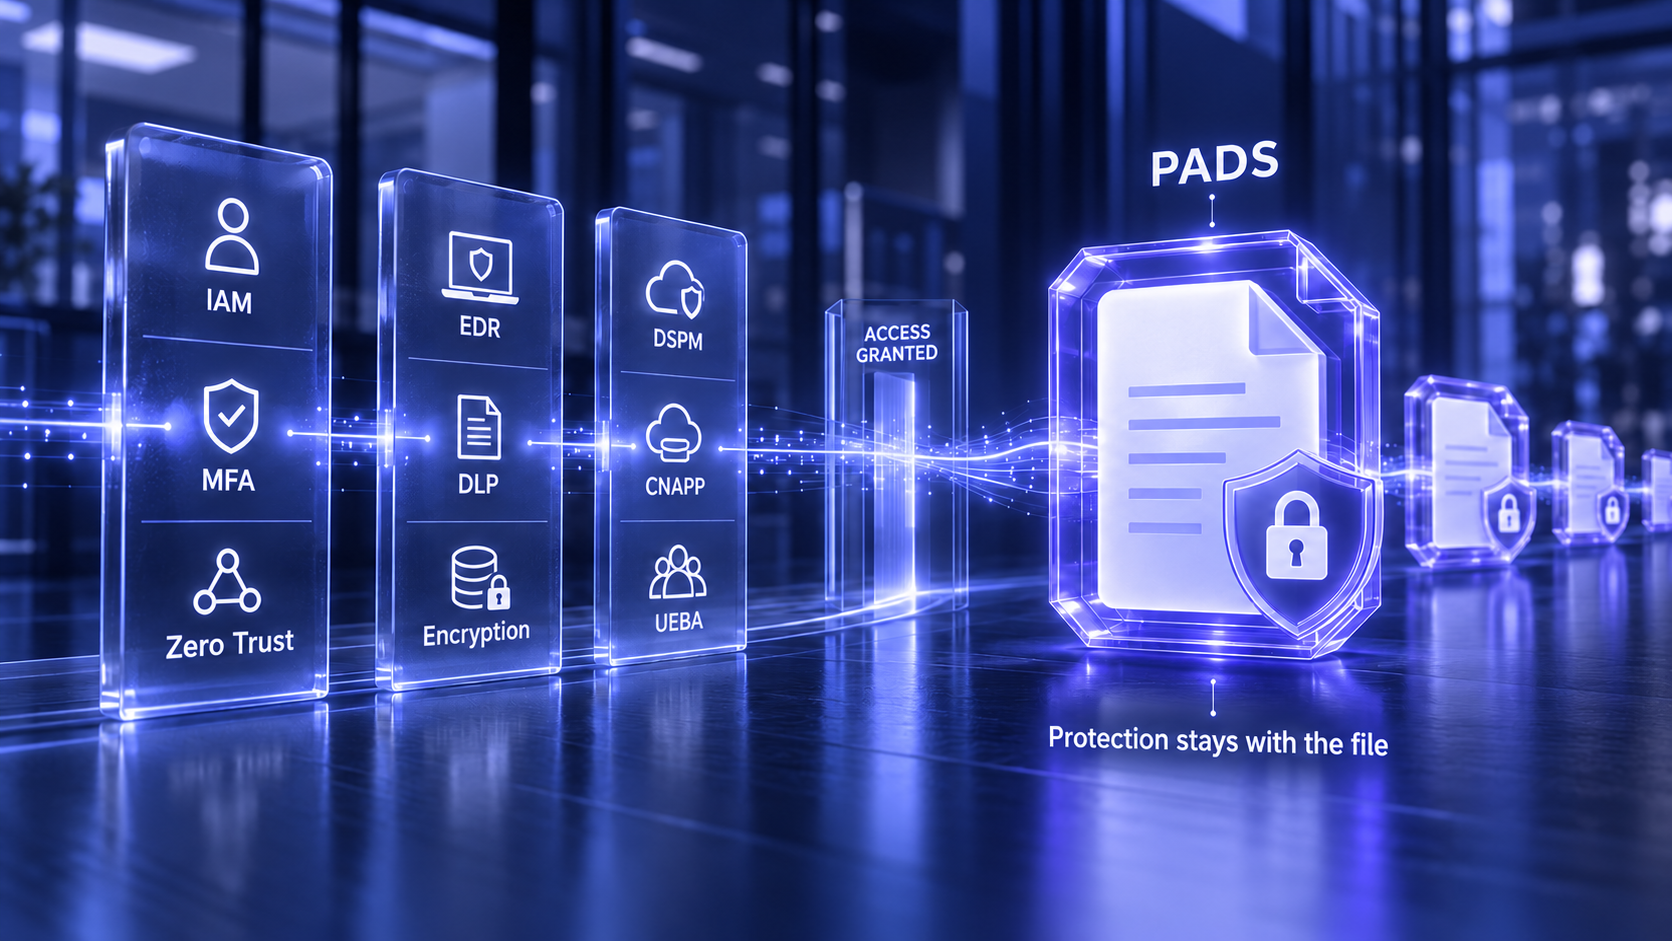
Post-Access Data Security enforces protection at the file level, independent of access method. Files remain encrypted even after authentication. Policy evaluation continues after login. Data protection does not dissolve once credentials are accepted.
This produces a fundamentally different financial outcome when a breach occurs.
Stolen files remain encrypted. Exfiltrated data is unreadable. Credential compromise does not automatically lead to disclosure. Breaches become operational events rather than financial catastrophes.
From an economic standpoint, this is loss elimination.
Security spending typically aims to make breaches less likely. PADS makes breaches less costly. That distinction is the difference between a defensive expense and a strategic investment.
Why PADS Aligns With Modern Reality
Security leaders increasingly recognize three truths they cannot engineer around.
First, identity compromise is inevitable. Credentials are phished, reused, replayed, misused, and stolen at scale. This is not a failure of IAM. It is a condition of operating in a connected economy.
Second, data is everywhere. SaaS platforms, collaboration tools, shared drives, cloud storage, third parties, and supply chains have dissolved any meaningful perimeter around information.
Third, compliance does not prevent data theft. It documents effort. It does not enforce outcomes.
PADS aligns security spending with these realities. It assumes compromise and protects the data anyway.
That makes it one of the few security investments that delivers immediate value, scales across environments, and strengthens governance conversations at the board level.
Protect the Asset, Not Every Attack Vector
Traditional security strategy attempts to neutralize risk one vector at a time. Phishing defenses for phishing. Insider risk tools for insiders. CASB for SaaS. DLP for data movement. Third-party risk platforms for vendors.
The result is tool sprawl, operational overhead, and diminishing returns.
PADS takes a different approach. It protects the asset attackers actually want.
Instead of asking which tool is needed for each attack type, leaders can ask a more durable question:
What protects our data no matter how access occurs?
That shift simplifies strategy and concentrates spend where it matters.
One Investment. Multiple Risk Classes Neutralized.
Because PADS operates after access is granted, it directly mitigates the most common and costly breach scenarios without requiring a constellation of point solutions.
Secure Sharing and Third-Party Risk
Most data exposure today occurs through legitimate sharing with partners, vendors, consultants, and customers. Traditional controls lose enforcement once files leave the environment.
With PADS, files remain encrypted wherever they go. Policies travel with the data. Access can be revoked instantly. Third parties never possess usable data outside approved conditions.
Third-party risk is contained at the data layer rather than managed through contracts and trust.
Insider Misuse
Insider misuse is difficult to prevent because insiders already have access. PADS limits what authorized users can actually do with data. Copying, exporting, and misuse outside policy silently fail.
Misuse becomes self-limiting by design, without intrusive surveillance or behavioral scoring.
Phishing and Credential-Based Attacks
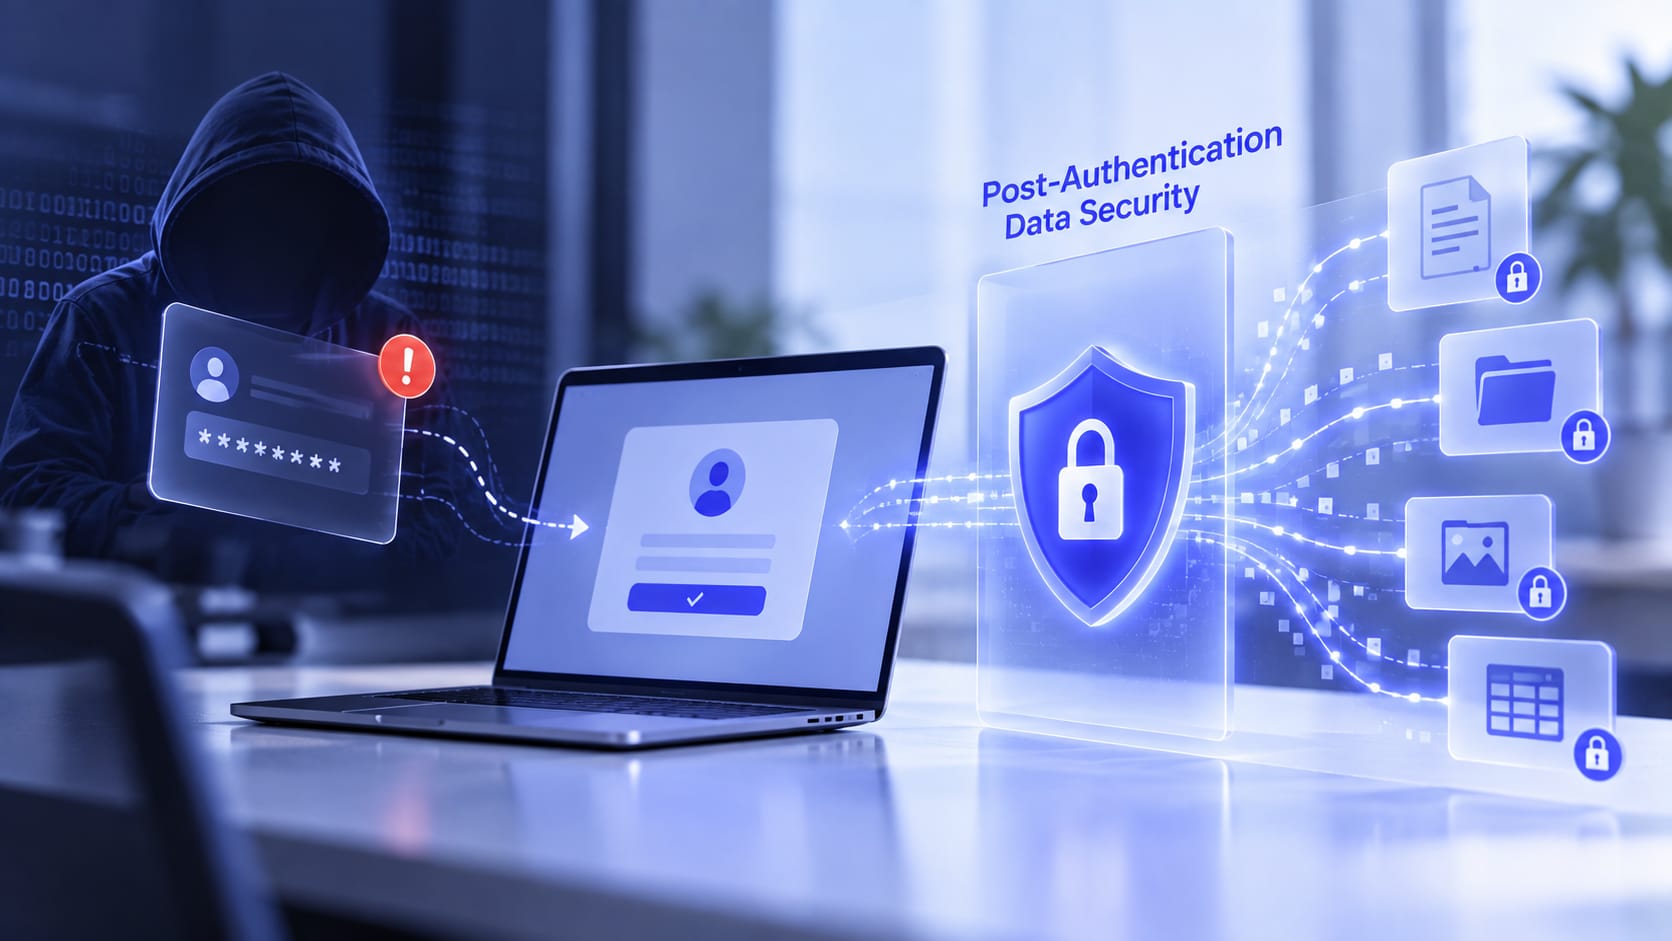
Phishing succeeds when stolen credentials lead to readable data. PADS breaks that chain. Credentials may still authenticate, but files remain encrypted unless conditions are met.
Phishing becomes an authentication issue, not a data-loss event.
SaaS and Application Credential Abuse
SaaS platforms assume authenticated access equals trusted access. PADS does not. OAuth abuse, API key theft, and session hijacking no longer result in mass exposure because the data itself remains protected.
Supply Chain Compromise
When vendors are compromised, shared data is often exposed. PADS ensures downstream access does not translate into downstream risk. Compromised partners do not expose your data.
A Simpler and More Economical Security Strategy
Security stacks became complex by solving problems one vector at a time. PADS reduces complexity by protecting the thing all attacks converge on.
For organizations early in security maturity, this means faster risk reduction, fewer tools to manage, and immediate protection without re-architecture.
For mature organizations, it means eliminating the most expensive failure mode their stack still allows.
In both cases, the return is measurable.
Quantifying Return on Security Spend
The largest breach cost drivers are well documented. Incident response. Legal fees. Regulatory fines. Settlements. Customer attrition. Insurance premium increases. Long-term reputational damage.
When stolen data is unreadable, many of these costs are reduced or avoided entirely.
That is the core ROI driver: lower breach impact, not just lower breach probability.
PADS also improves insurance economics by enabling provable containment. Organizations that can demonstrate unreadable data face better underwriting, fewer exclusions, and less claim friction.
It simplifies compliance by providing clear evidence of persistent protection, reducing audit scope and compensating controls.
And critically, it can deliver this value without needing to displace existing investments. PADS can integrate above IAM, Zero Trust, EDR, DLP, and cloud security tools. It does not require write-offs or workflow disruption.
Why PADS Makes Sense at Any Scale
For large enterprises, breach impact scales with data volume and regulatory exposure. PADS caps downside risk by ensuring that even successful attacks cannot extract usable data.
For small and mid-sized organizations, a single breach can be existential. PADS provides enterprise-grade protection without enterprise complexity, enabling survival, credibility, and deal confidence.
When security resources are limited, investing where loss actually occurs delivers disproportionate value.
Real Security ROI Comes From Protecting Value
Cybersecurity spending continues to rise because losses continue to rise. The industry has optimized for chasing threats instead of protecting value.
Post-Access Data Security changes that equation.
By securing data itself, independent of access method, environment, or identity state, PADS by PostAuth ensures that breaches, insider misuse, and third-party failures do not become data-loss events.
This is why PADS delivers superior return on security spend. One control neutralizes multiple high-impact risks. Loss is reduced at the source. Tool sprawl becomes less necessary. Governance outcomes improve immediately.
Security ROI is not created by owning more products. It is created by ensuring that data cannot be stolen, misused, or monetized, no matter how access occurs.
That is the shift from chasing threats to protecting value.
And that is where cybersecurity finally becomes economically defensible.