Data Protection
Why Compliance Still Isn’t Protecting Financial Data?
Compliance doesn't stop breaches; most victims were fully compliant when hit. PADS by PostAuth fills the gap by securing data after login, turning regulatory checklists into actual data protection.
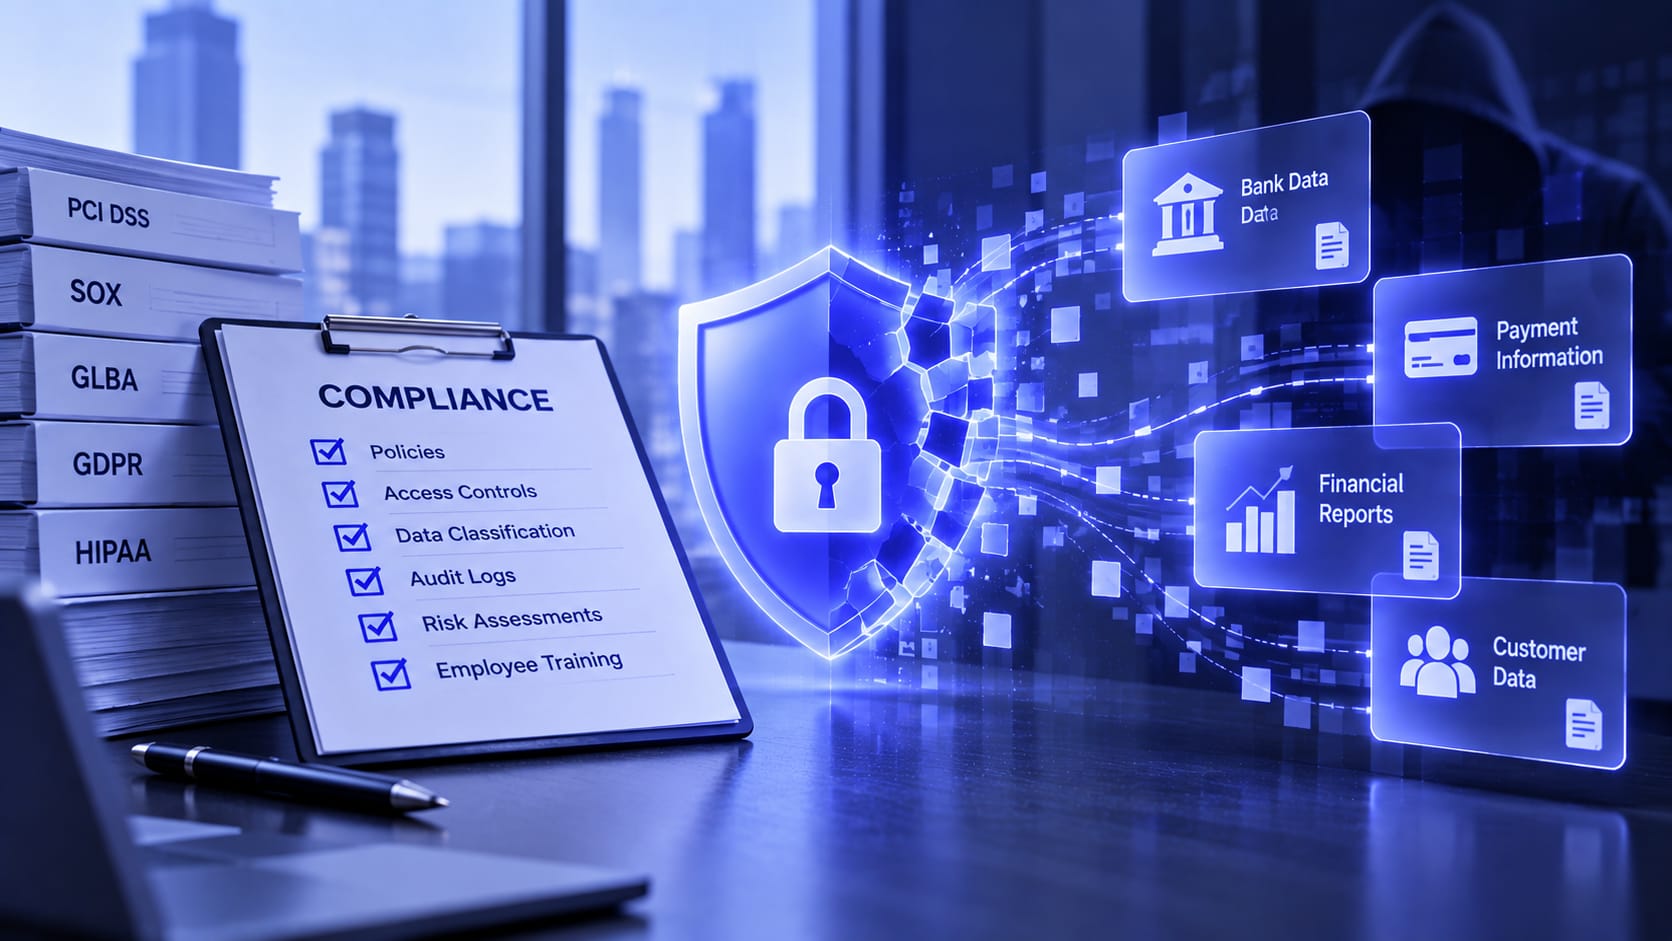
Every major financial institution with a headline-grabbing breach on the books was fully compliant at the time of compromise. Capital One. Morgan Stanley. JPMorgan. Equifax. Robinhood. First American Financial. The pattern is consistent and deeply uncomfortable.
Financial services firms operate under some of the most demanding cybersecurity regulations in the world. Think SEC disclosure rules, NIST frameworks, FFIEC examinations, PCI requirements. These standards form the backbone of modern financial cybersecurity programs and require extensive governance, documentation, and technical controls.
And yet data theft continues.
This reality has become harder to ignore following recent amendments to SEC Regulation S-P, which significantly expand expectations around safeguarding customer information. The amendments require comprehensive written incident response procedures, clear plans for detecting and containing unauthorized access, and mandatory notification when sensitive customer data is exposed.
These updates reflect an important shift. Regulators are no longer satisfied with policy documentation alone. They expect institutions to demonstrate that controls actually protect customer data.
But even with these stronger requirements, compliance still does not prevent modern data theft. That gap exists because today’s attacks exploit a failure mode that regulations were never designed to address.
The Failure Mode Regulators Do Not Measure
Executives need to understand a critical distinction: Compliance frameworks measure the environment. Attackers target the data. See the gap?
Every major financial breach followed the same sequence. Controls worked as designed. Audits were passed. Systems were hardened. And the data was still taken.
Modern attacks do not bypass controls. They turn them against you.
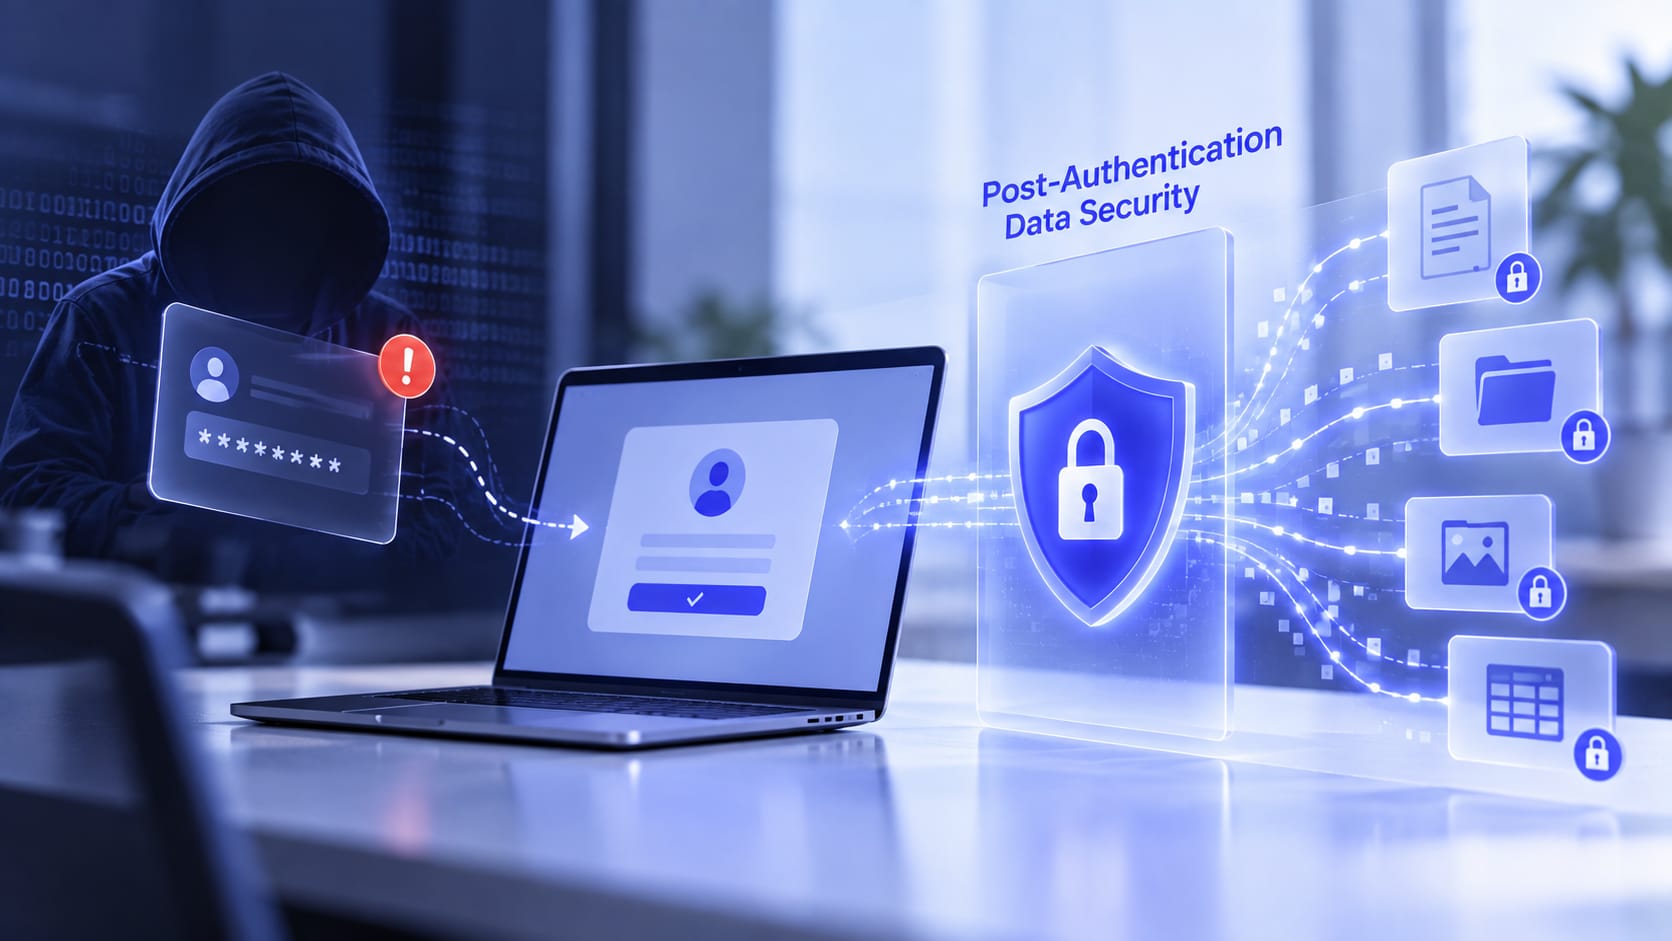
The pattern is simple and repeatable. Attackers obtain valid credentials. They authenticate successfully. Files decrypt automatically. Data is accessed in cleartext and exfiltrated. The organization remains compliant and devastated at the same time.
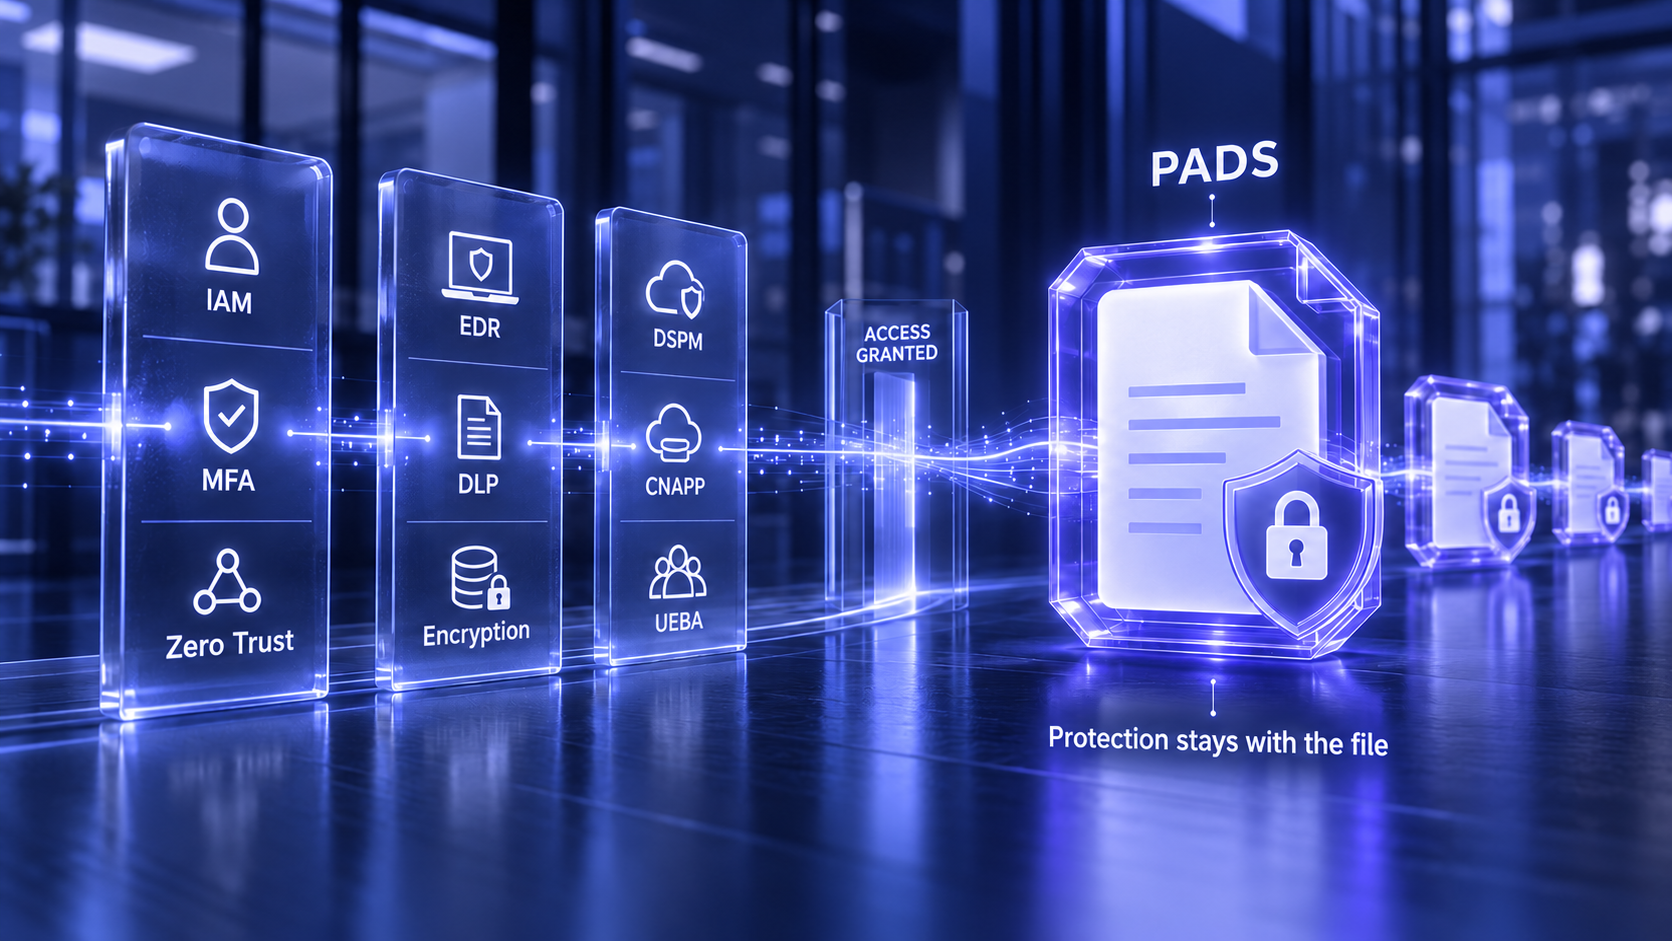
In most financial cybersecurity stacks, even the most mature ones, there is a fundamental architectural failure. The moment a valid username and password are used, meaningful data protection ends.
Encryption disengages. Access controls trust the session. Monitoring becomes reactive rather than preventive.
This is the post-access data security gap. And it is the moment attackers understand better than defenders.
Why Compliance Frameworks Miss This Gap
Every major regulatory and standards body focuses on protecting systems, identities, and sessions. Understand that SEC rules emphasize governance and disclosure. NIST frameworks catalog technical and administrative controls. FFIEC guidance addresses risk management and oversight. PCI enforces strict encryption requirements for cardholder data.
What none of these frameworks require is persistent, file-level protection once a user authenticates.
Encryption at rest protects data if a physical device is stolen. Encryption in transit protects data moving across networks. Neither protects files once a valid login occurs.
As a result, over 80 percent of modern data theft now occurs after successful authentication. Regulations measure whether systems are configured correctly. Attackers measure whether data decrypts when they log in. One addresses yesterday’s threats. The other defines today’s reality.
Why Compliance Alone Is No Longer Defensible
Financial institutions must now confront a difficult truth. Compliance sets the floor for acceptable behavior. It does not define effective data protection.
The financial impact of data theft far exceeds regulatory penalties. Customer churn, class action litigation, incident response costs, recovery operations, insurance premium increases, and reputational damage routinely dwarf the cost of compliance.
At the same time, customer and counterparty expectations are rising faster than regulations. Financial services contracts increasingly require proof of secure data handling, modern identity architectures, and demonstrable controls over sensitive files. Compliance alone is no longer sufficient to win business.
Recent SEC disclosure requirements further raise the stakes. Boards and executives must now publicly describe cybersecurity risk management effectiveness and material impacts. A breach where controls worked but data was taken is becoming indefensible to investors.
Why Post-Access Data Security (PADS) Changes the Equation
PADS addresses the exact failure mode that compliance frameworks and audits overlook.
It starts by asking a different question. What happens when an attacker logs in successfully?
In a Post-Access Data Security model, data remains encrypted even after authentication. Access to sensitive files is continuously evaluated based on identity, device, and context. Policies travel with the data wherever it goes. If files are exfiltrated, they remain unreadable and unusable.
This architectural shift changes the outcome of breaches. Credential compromise no longer guarantees data loss. Insider misuse becomes containable. SaaS and cloud data remains protected outside the perimeter.
Most importantly, PADS delivers something compliance never has. Provable data protection outcomes.
The Standard Financial Leaders Must Exceed
Compliance will always matter. It prevents penalties and establishes baseline hygiene. But it cannot be the end goal.
Financial institutions must exceed regulatory requirements because attackers already have. They operate after authentication, inside trusted sessions, against data that decrypts automatically.
PADS closes the post-authentication gap that regulations do not cover, audits do not test, and attackers consistently exploit.
Conclusion
Financial firms can be fully compliant and still catastrophically exposed. The regulations set the floor. Attackers set the bar.
To protect data rather than just systems, financial institutions must adopt Post-Access Data Security. It is the only approach that survives credential compromise, neutralizes insider threats, and turns breaches into contained events instead of existential failures.
Compliance prevents penalties. PADS by PostAuth prevents data loss. And in today’s financial threat landscape, the difference matters.